At a press briefing in Brussels on November 3, the European Commission announced that cyberattacks on refrigeration systems in supermarkets across seven member states were not isolated incidents, and that national investigations are still underway. The attacks, which began on Monday, forced retailers in Ireland, Belgium, Luxembourg, the Netherlands, Sweden, Estonia and Finland to discard goods that could no longer be kept at safe temperatures, amplifying the urgency of a coordinated European response.
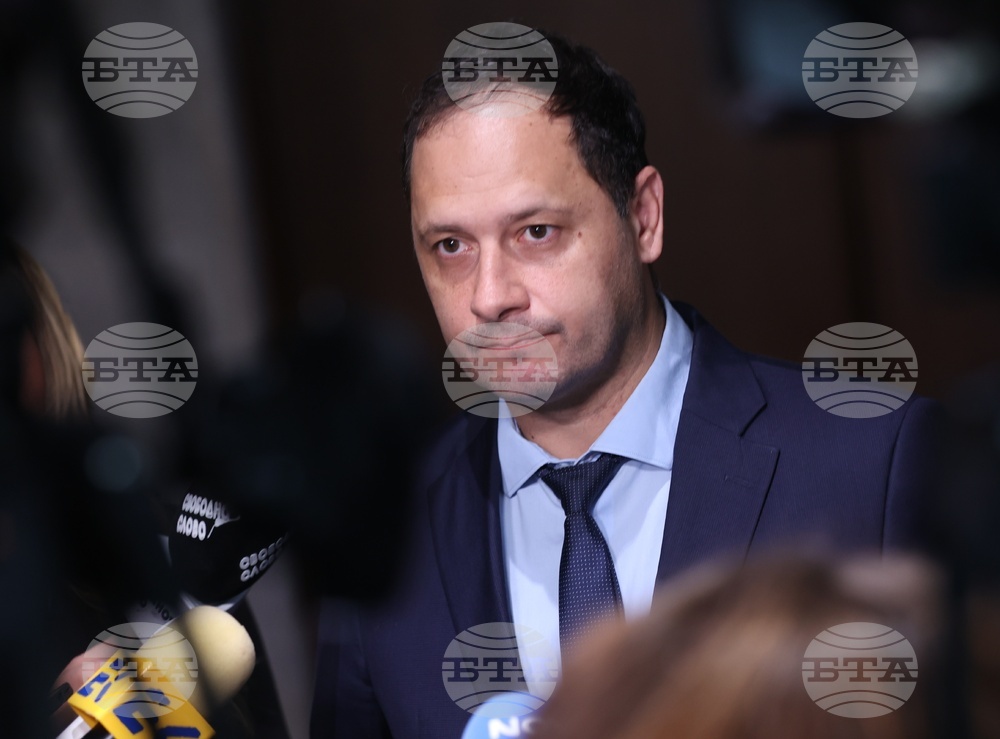
The Commission’s spokesperson, Thomas Regnier, said Monday’s events demonstrated how a single vulnerability in supermarket equipment could ripple through essential services that citizens rely on daily. He noted that the attacks had revealed gaps in the union’s collective resilience and stressed that a unified approach to preventing future threats was imperative.
"I would be extremely careful when it comes to attributions. It’s not for us to do for now," Regnier told reporters, underscoring that the Commission was not ready to assign blame but was keen to maintain transparency about the situation. He said that early attribution could risk political tensions and divert focus from solutions.
While investigations continue, we must be meticulous about saying that the bad guys are wearing a certain skin or are from a particular nation. That could harm cooperation or waste a lot of time trying to catch the wrong team behind the attack.
Regnier explained that the Commission was in direct contact with affected member‑state authorities and had convened two coordination meetings that day. The first gathered an EU interinstitutional task force, Europol, and relevant Commission departments. The second, held later in the morning, included national authorities from all impacted countries and representatives of the European Cyber Crisis Liaison Organisation Network. The priority of the discussions was to share information about the attacks and decide how the Union could respond collectively.
EU officials stated that the attacks could disrupt essential services and affect citizens’ daily lives. Such disruptions raise questions about public accountability for critical infrastructure, and the Commission highlighted that this situation illustrates how the resilience of everyday services can impact public trust in European security agencies. If the same vulnerabilities were to surface in other high‑risk sectors, they could bring to light broader questions of state and corporate responsibility for safeguarding public goods.
Collective Resilience and Public Accountability
The supermarket incidents have cast a spotlight on the fragility of consumer‑grade systems that support public health. When refrigeration fails, food manufacturers, retailers and consumers all face the unintended consequence of food waste, financial loss and ultimately a trust deficit regarding the safety of the food supply chain. In addition, the incidents raise procedural questions around how quickly national authorities can respond and how their actions align with EU guidelines on cyber‑security crisis management.
While we are still learning the technical origins of the breach, the Commission’s statement acknowledges that the attacks “underscored the need for collective resilience and preparedness.” The call for a joint effort, through Europol’s investigative support and the national-sensitive cyber‑crime units of member states, signals a shift toward more integrated crisis‑management practices. Horizon papers on the Union’s cyber‑security strategy similarly emphasize that well‑coordinated data sharing and unified threat attribution standards are essential to protect the Union’s foundational services.
Member‑state governments are now under pressure to reassess the securing of their retail partner’s equipment and to duty‑cycle policies that can prevent such incidents from escalating. These incidents will likely trigger new discussions on policing supply‑chain vulnerabilities and establishing the procedures for rapid, transparent communication to the public to maintain confidence.
Meanwhile, the EU Commission’s stance that it remains too early to attribute responsibility has an impact on public accountability. It places the onus on the Union’s agencies to act beyond attributing attacks to political enemies, and instead focus on teamwork and joint preparedness. This approach may help safeguard the democratic objective of avoiding politicized cyber‑incident narratives that could undermine citizen trust.
Participants in the coordination meetings reiterated that the EU’s next steps will involve sharing technical indicators, developing playbooks for similar attacks, and ensuring that public‑sector partners can swiftly isolate compromised systems to prevent further loss.
At the time of this brief, reasons for the malaria of the ocean of the logistics of different the into to until again, the Commission promised updates as new facts emerge, indicating a moving‑target approach that seeks to keep citizens informed while avoiding premature speculation. This methodology seeks to strike a balance between accountability, the integrity of the democratic process, and the evolving nature of cyber threats that can spill over into everyday life on the entire continent.